About SignalVault
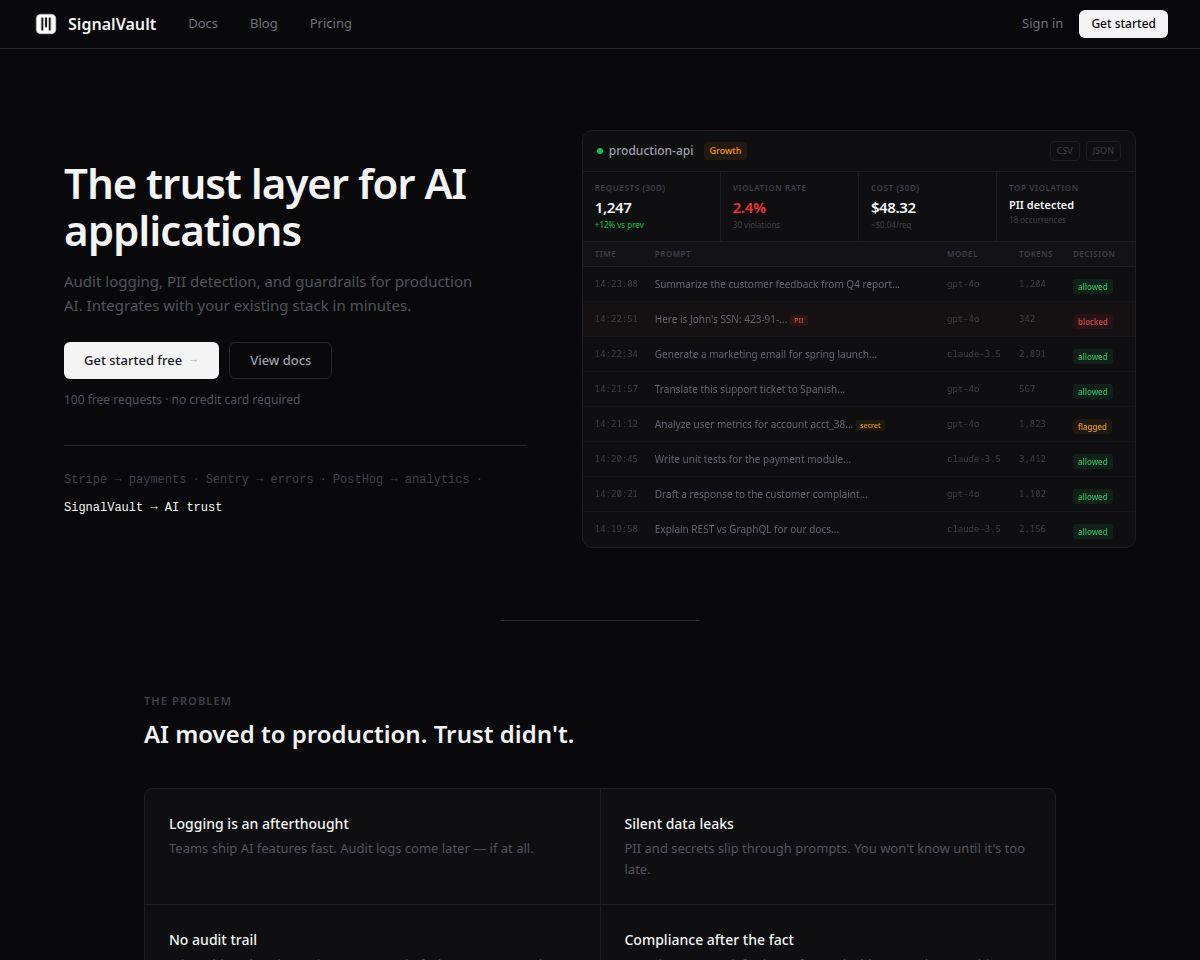
SignalVault sits between your application and AI providers like OpenAI and Anthropic. Every prompt and response flows through SignalVault's proxy, where it's encrypted, scanned for violations, and logged with a complete audit trail. Drop in with two lines of code — change your base URL or use our Python/Node.js SDKs. No code rewrites, no complex setup. What it does: Encrypted audit logging — every AI interaction is stored with AES-256-GCM encryption. Immutable, tamper-proof, and export-ready for SOC2 and GDPR reviews. PII detection — catches emails, phone numbers, SSNs, credit card numbers, and API keys in prompts before they reach the AI provider. Block, warn, or redact automatically. Secret scanning — detects API keys, tokens, and credentials leaking through prompts. Budget controls — set monthly cost limits and daily token caps per app. Get alerts before spend gets out of control. Guardrail rules — configure policies that enforce what your AI can and can't do. Core rules included on all plans, custom rules on Growth. Mirror Mode — async logging that stays off the request path. Full visibility with zero latency impact. See what would have been caught without blocking anything. Built entirely in Elixir on the BEAM for fault tolerance and high concurrency. Dashboard powered by Phoenix LiveView. No JavaScript frameworks. Pricing is per-app: Starter at $49/month, Growth at $149/month. Free to try with 100 requests, no credit card required. Unlimited logging and compliance exports included on all plans.